
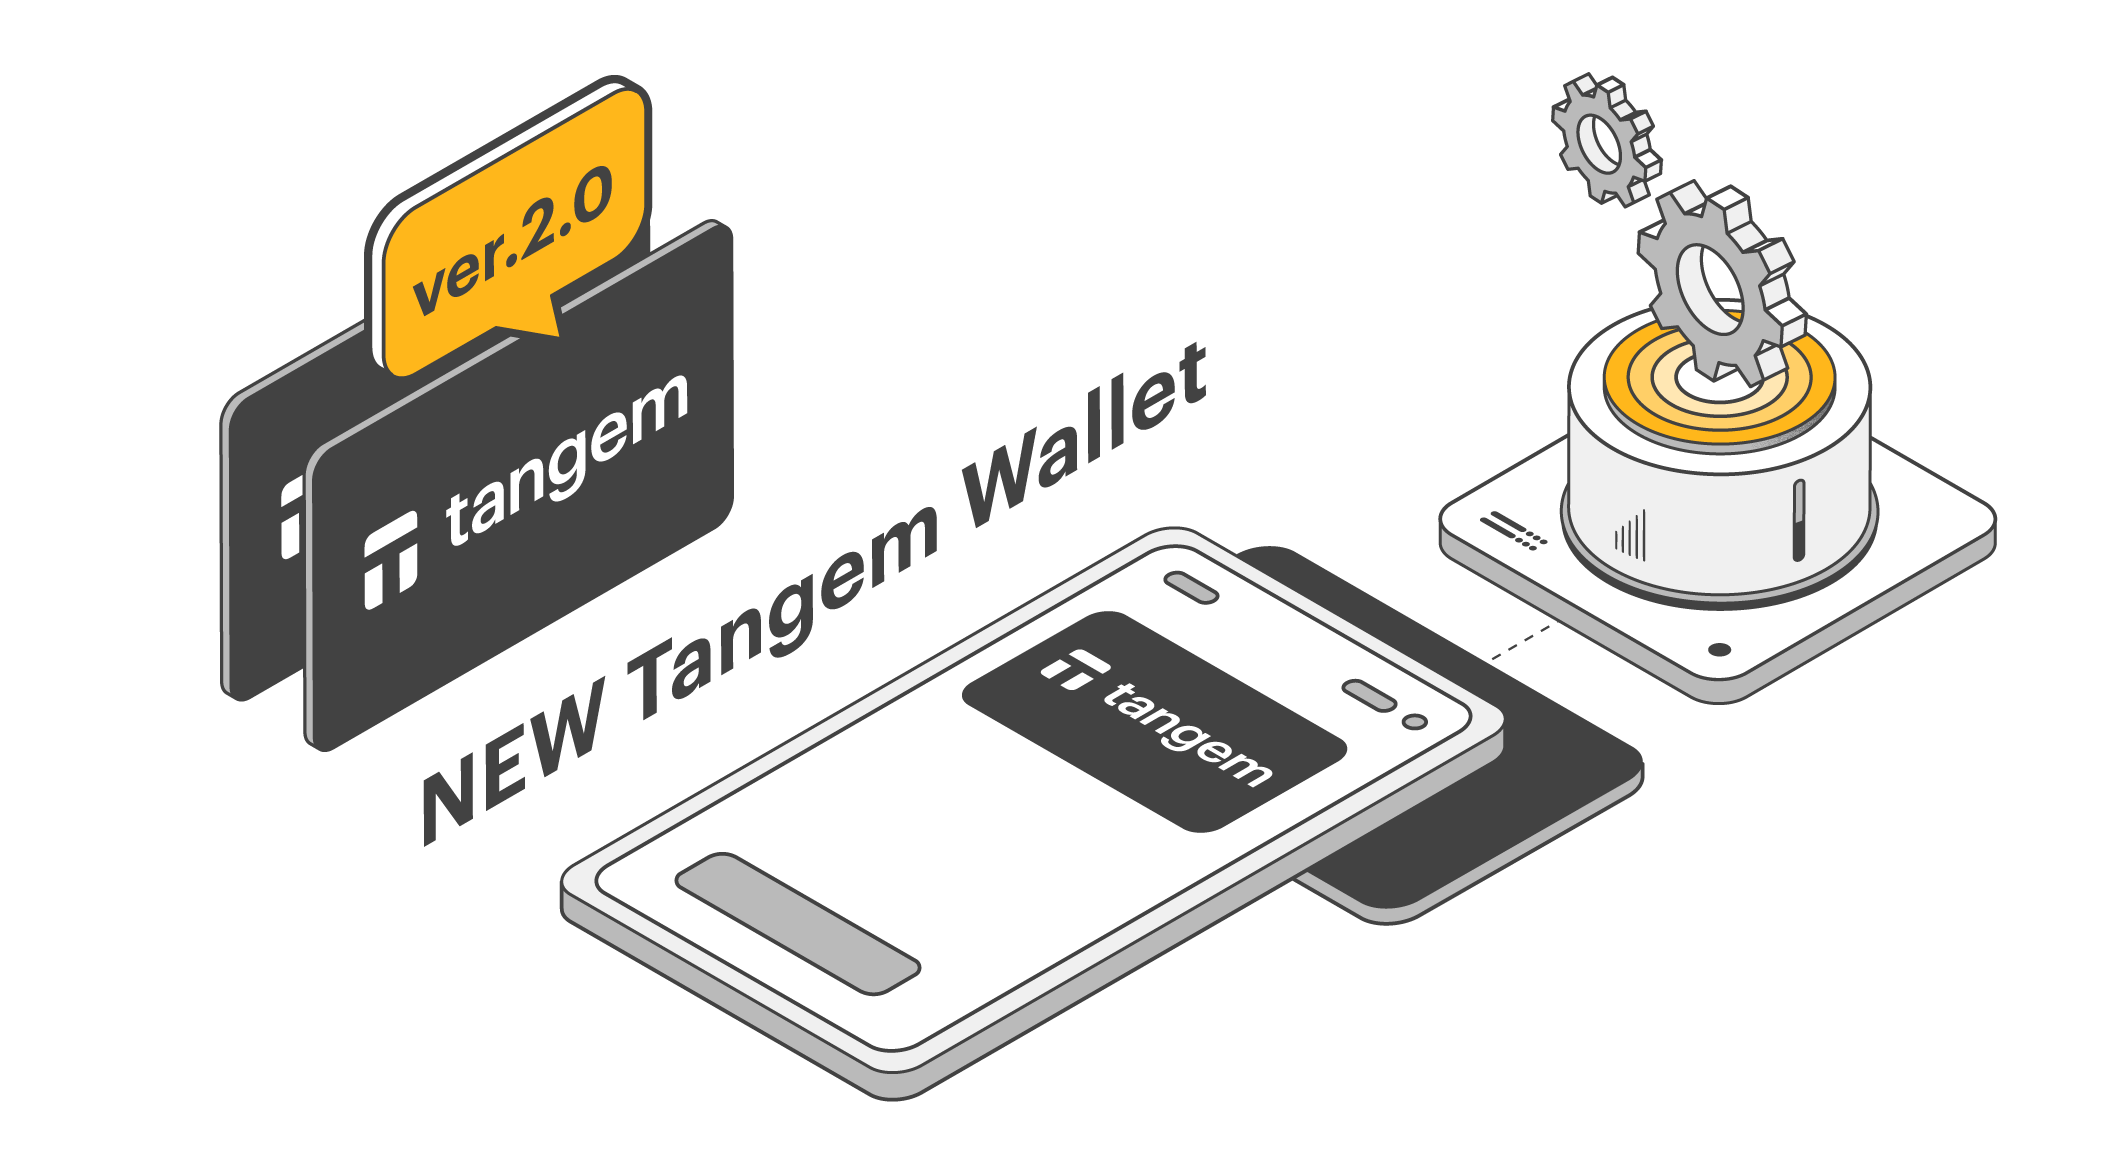
Whoa! I still remember the first time I tapped a tiny card to my phone and watched an account unlock — felt like sci-fi. My instinct said this was neat, almost suspiciously neat. Hmm… something felt off about the size-versus-security ratio at first. But then the practical part of me kicked in: I carry a wallet everywhere, and why can’t my crypto live there too? Initially I thought hardware wallets had to be clunky devices with screens and cables, but the Tangem approach made me rethink assumptions about what “cold storage” can look like.
Here’s the thing. NFC wallets changed the script. A card you tap is faster than fumbling with a seed phrase on a piece of paper, and it’s less intimidating for newcomers. Seriously? Yep — the UX is that smooth. There are trade-offs, of course, and after some tests (and a few mistakes on my end) I started mapping the limits, not just the benefits. On one hand, having a card that fits in a wallet is obvious convenience; on the other hand, the security guarantees depend on tamper-resistance and the backup strategy you choose, which not everyone discusses.
How a tangem card fits into my daily routine
I used the tangem card as my main test device for a couple months. At first I treated it like a novelty. Then it became habitual. Quick anecdote: I once left my physical wallet in a coffee shop (rookie move) and didn’t panic about my crypto, because the card requires a physical tap and also the wallet app with a PIN. That made me breathe a little easier. I’m biased toward simple designs, and this card nails ergonomics without forcing you into a hundred technical settings (which, honestly, I sometimes avoid anyway).
My gut feeling when testing was: this reminds me of contactless bank cards, but under the hood it’s very different. The private keys never leave the card. That matters. Actually, wait — let me rephrase that: the private keys are generated and stored on a secure element inside the card and signing happens internally, so you never export the keys into your phone. That’s a core security win, though it doesn’t make everything bulletproof. There are scenarios where a multi-sig hardware approach still makes more sense, particularly for institutional or very high-value holdings.
On usability: tapping an NFC wallet is low friction. Tap. Approve a transaction. Done. There were moments I wished for more advanced transaction previews on the card itself (there’s no full display like on some dedicated hardware devices), which sometimes made me rely on the mobile app’s confirmation UI. That part bugs me—it’s a UX compromise between portability and on-device visibility. (oh, and by the way… I’m not 100% a fan of tiny confirmation screens on phones either.)
Security-wise, here’s where System 2 thinking takes over. Initially I thought physical form-factor alone was risky, though then I dug into tamper-evidence design and secure elements used by cards like this. They use dedicated chips that resist extraction attempts, and the business model is different: a single-use, sealed card that you treat like a bank card. On the other hand, you must plan for loss, damage, or wallet app compromise. So the design philosophy nudges you toward treating the card as a primary key-holder with a separate recovery method — not an all-in-one safety blanket.
So what are the recovery options? Some people write down a mnemonic, others use multiple Tangem cards (very very popular among users who want redundancy), and some pair the card with custodial backup solutions. My approach was to use two cards and one encrypted off-site backup — redundant without being obnoxiously fragile. On the subject of backups: create a routine. Seriously. If you rely on a single physical token and misplace it, your choices narrow fast.
I ran a few practical tests. Small transactions, large transactions, delayed confirmations, different phones (Android and iOS), and even a cheap NFC-enabled flip phone I had lying around (for the nostalgia). Most of the time the tap-and-sign flow worked flawlessly. On rare occasions, certain Android phones had short glitches with the NFC stack; a quick reboot fixed it. Not catastrophic, but worth noting if you’re the kind of person who travels and swaps devices often. My takeaway: test your setup before moving big amounts.
There’s also ecosystem maturity to consider. Tangem’s wallet integration has improved; third-party apps increasingly support card-based signing. That network effect matters. Initially I thought compatibility would be the bottleneck; though actually, the opposite happened — wallets adapted because users wanted convenience. That surprised me. But compatibility isn’t universal, so if you depend on niche chains or specialized DeFi protocols, double-check support before committing to any single card-only workflow.
On privacy: carrying an NFC card doesn’t make you invisible. Tap patterns, app usage, and on-chain activity can still be analyzed. If privacy is a high priority, you’ll need additional practices. I’m not pretending the card solves everything. My advice: use it as part of a layered approach — isolation, limited exposure, and prudent on-chain behavior. Also, remember that if the card is physically seized, an adversary still needs to pass the app’s security measures, but hardware attacks and social engineering are real risks.
Cost and lifespan are practical points people ask about. Tangem-style cards are relatively inexpensive compared with screen-equipped hardware wallets. They can be treated as semi-disposable in a sense — cheap enough to keep spare copies in secure locations. That changes risk calculus; you might prefer cheap redundancy over a single expensive device. Of course, if you want institutional-grade setups with multi-sig across geographically separated hardware, this card isn’t a full substitute.
One more thought about user behavior. People often overindex on features and underindex on habits. You can have the most secure card, but if you habitually approve suspicious transactions because your phone is compromised, that’s the real failure mode. My instinct said this would be a “set-and-forget” improvement; in practice it nudges you to be more deliberate, which I appreciate. There’s a mental benefit to tapping a card that feels almost ritualistic — small actions that reduce careless mistakes.
FAQ
Is a Tangem card secure enough for long-term storage?
Short answer: for most retail users, yes — it’s a strong option. The private keys stay on the secure element and signing happens on-card. Long answer: consider value, threat model, and backups. For institutional or extremely high balances, multi-sig across diverse hardware is still best.
What happens if I lose the card?
If you lose a single card without backup, recovery depends on how you set up the wallet. Use redundant cards or an encrypted recovery plan. I’m biased toward having spare cards stored separately — it feels safer to me.
Can someone clone the card by reading it with an NFC reader?
No — the card is designed so private keys cannot be read or exported via NFC. Transactions can be signed via the secure element only. Still, physical security and social engineering remain concerns.